Trust, verify, and the boundary of the product
Live registry rules, security controls, privacy, and a clear line: Oryxen is software, not a certifier.
Live registry. Controlled approvals.
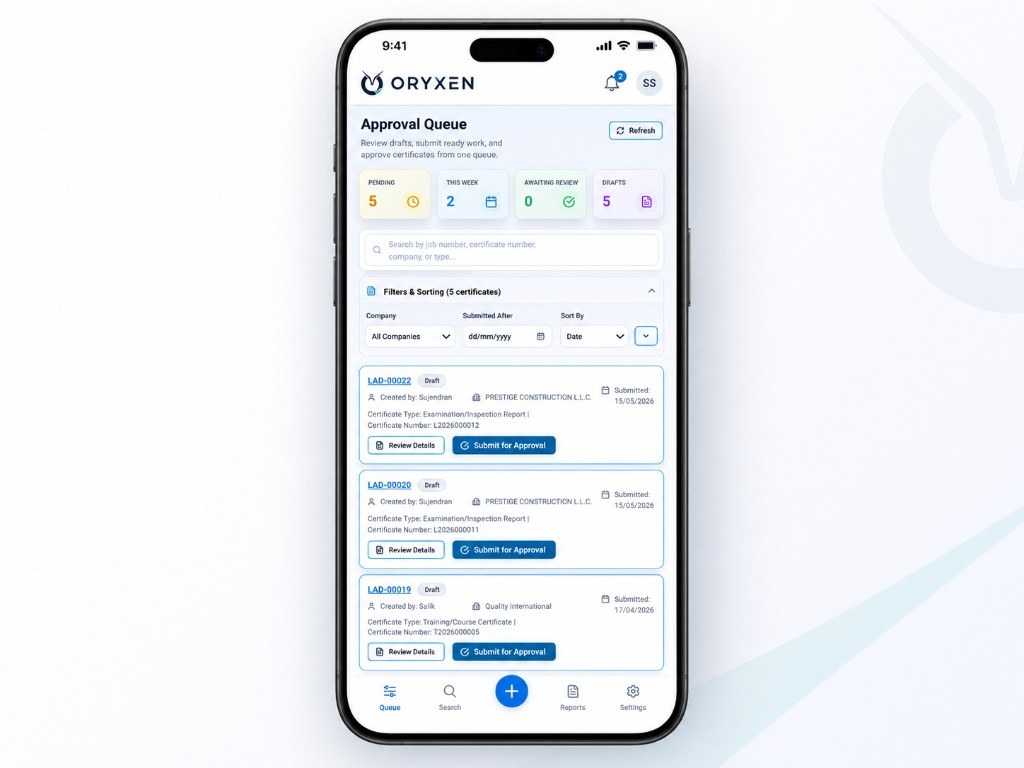
Public QR resolves issued / revoked / not found. Drafts stay private. Every submission and signoff stays inside a role-gated queue with a retrievable history.
Live verify
Public QR codes resolve against a live registry. Possible public states are issued, revoked, and not found. Draft certificates stay private and never verify as valid.
White-label verify shows the customer’s name. The market sees the issuer’s brand and domain, not Oryxen as the certifier.
Overview
This Trust and Security summary describes how Oryxen protects customer data and platform operations. It is intended for UAE and Pakistan customers evaluating or using the platform.
Security controls
Oryxen applies reasonable security controls suitable for SaaS workflow software, including role-based access, authentication controls, encrypted connections, secure file handling, audit logs, backups, restricted admin access, and environment separation where applicable. Formal ISO 27001 or SOC 2 certificates are not claimed on this site.
Oryxen may log security events and user activity to investigate misuse, support audits, and protect the platform.
Customer admin responsibility
Customer admins are responsible for assigning correct roles, removing inactive users, protecting credentials, verifying document approvals, and managing internal access policies.
Customers should promptly notify Oryxen if they suspect unauthorized access, credential compromise, or misuse of platform records.
Data Processing Agreement summary
For B2B customers, the customer generally acts as the controller or data owner, and Oryxen acts as a processor or service provider for data uploaded into the platform.
Oryxen processes customer data only to provide the service, support users, secure the platform, troubleshoot issues, generate reports/certificates, maintain backups, and comply with lawful instructions. Oryxen does not sell customer data.
Customer data may include personal data, signatures, engineer information, client information, inspection evidence, uploaded files, certificates, approval logs, and business records.
Subprocessors
Oryxen may use approved vendors to host, operate, monitor, secure, or support the platform. Example subprocessors may include cloud hosting/infrastructure, database hosting/backups, email delivery, file storage, analytics, error monitoring/logs, AI/OCR processing, and business tools such as Google Workspace or equivalent.
Oryxen maintains an updated subprocessor list. Customers may contact Oryxen for the current list.
Oryxen remains responsible for selecting vendors carefully and requiring reasonable safeguards from subprocessors.
Security incidents
If Oryxen becomes aware of a security incident affecting customer data, it will investigate, contain the issue where possible, and notify affected customers in line with contractual and legal obligations.
Security contact: security@oryxen.com
Accreditation and licensing note
Oryxen is software. It helps companies manage workflows, documents, approvals, reports, and certificates. Oryxen does not itself grant accreditation, certify equipment, approve inspectors, or replace the customer’s regulatory obligations. Oryxen is not PNAC, EIAC, or ENAS.
Customers remain responsible for ensuring that their certificates, inspection reports, letterheads, accreditation marks, engineer approvals, and issued documents comply with the rules of applicable bodies in the UAE, Pakistan, and any other jurisdiction where they operate.
What we do not claim
This is a high-level public overview for buyers evaluating the product. We do not claim ISO 27001, SOC 2, blockchain, or country-level data residency unless a signed contract says so. Specific commitments such as SLAs, subprocessors, and data processing addenda are provided during customer contracting where applicable.
Handoff, not a 20-module ERP
- CSV / Excel export for your accountant
- QuickBooks / Xero / Tally — planned accountant handoff
- Email notifications and configurable alerts
- iCal feeds and optional Outlook / Microsoft 365 calendar sync
- Web push and PWA-friendly engineer views
- REST APIs for Enterprise tenants
CSV/Excel to your accountant today. QuickBooks, Xero, and Tally as a later handoff. Not SAP, payroll, or LIMS.
See how issuance would run on your types.
Book a demo. We’ll walk the loop — job, site evidence, approval, branded PDF, live verify — on your certificate families, not a generic deck.
No credit card · 30-minute walkthrough · Google Meet follow-up